Five-pillar architecture
Contracts, trust boundaries, lifecycle, failure, recovery and evidence requested per pillar.
Qualified technical evaluators receive a revocable, client-confidential GitBook site and an immutable dated PDF snapshot tied to the exact architecture, claims and component versions under review.
The assurance experience is more detailed than the public publication but remains sanitised: representative declarations and contracts, never private repository links, credentials or exploitable client detail.
Five pillars, trust boundaries, data flows and compatibility.
Identity, IAM, encryption, secrets, network and change control.
Current evidence, limitations, NFRs, recovery and acceptance.
Responsibilities, handover inventory and client operating authority.
Structural checks are valuable, but they are not described as an accepted client production deployment. A later evidence level is earned only by the environment and acceptance it actually represents.
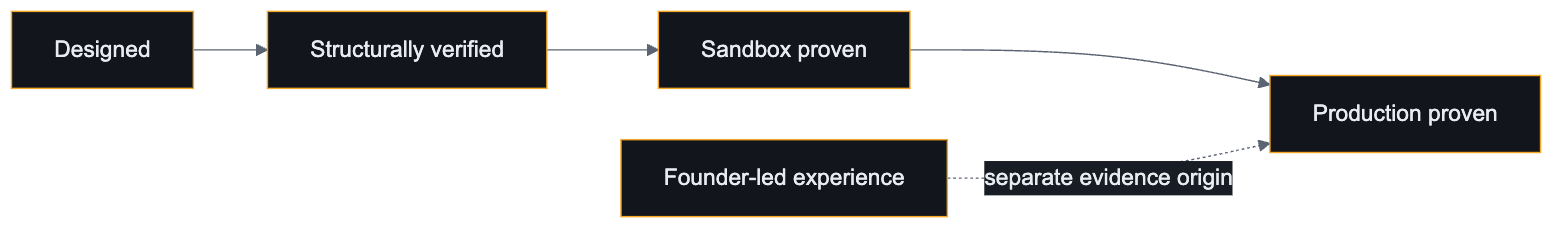
Founder-led experience is a separate evidence origin; it is not relabelled as a Substrada engagement.
Contracts, trust boundaries, lifecycle, failure, recovery and evidence requested per pillar.
Shared responsibility, identity, encryption, secrets, network controls and sensitive-data paths.
Readiness, controlled order, change control, objective acceptance and version compatibility.
Availability, performance, reliability, security, operability and acceptance methods.
Current evidence, release-scoped claims, known limitations and the evidence required next.
Component inventory, runbooks, access transition, enablement and client-owned operation.
Each active evaluation receives a named access owner and expiry. Its PDF snapshot includes a manifest and checksums. Corrections produce a new version so a reviewer can always identify what they evaluated.